Get C2PA conformant with our new guide
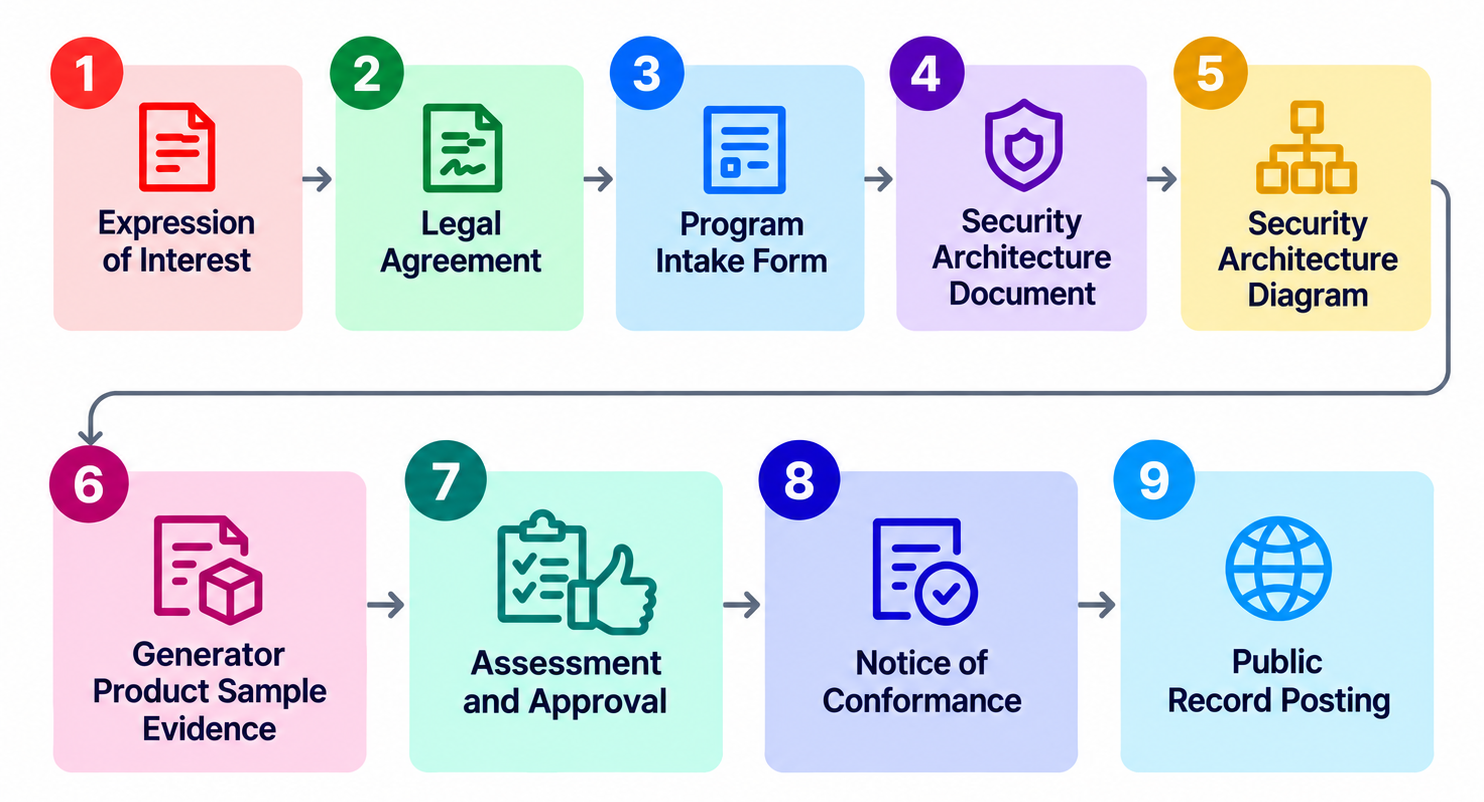
If your product signs or validates Content Credentials, then you should be aware of the C2PA Conformance Program. Going through the program to get your product approved as a conforming product:
- Assures that your product correctly implements the C2PA’s standard and meets a minimum bar of security and interoperability.
- Enables you to get a trusted claim-signing certificate issued by a certificate authority (CA) that’s on the C2PA Trust List.
- Means that your product will be included on the C2PA conforming products list, visible through the C2PA Conformance Explorer.
- Means that your product will be included in the CAI’s Ecosystem Explorer (launching soon). Apply here to include all the information you would like displayed.
This summer, C2PA released an updated version of the C2PA conformance program (version 0.2). We’re taking this opportunity to release a step-by-step guide to help you pass conformance, along with an open-source example app. Whether you're going through conformance for the first time or updating a product that passed a previous version of the program, these resources will help you succeed.
Implementer's guide
The new Guide to C2PA conformance for product implementers walks you through the full process for a backend generator product applying for Assurance Level 1. It covers everything from completing the expression of interest and intake forms through documenting your security architecture and generating signed interoperability assets for review. It finishes with the final assessment and approval of your product.
Conformance example app
The implementer's guide is based on a working, open-source signer app called conformance-example-app. This app accepts an uploaded JPEG image file, crops the image, and then adds and signs Content Credentials. Assertion generation, manifest construction, and claim signing all happen server-side, with the signing key held in a cloud KMS.
Because the app is open source, you can see exactly how each section of the security document maps to real code and infrastructure.
Get support on the CAI Discord
Join the CAI Discord server if you haven’t yet done so. The server is an open forum with a number of channels where developers discuss standards, C2PA conformance, how to use the CAI’s open-source SDK, and many other implementation questions.